Business VPN vs Zero Trust Network Access
An employee needs one internal dashboard, and the VPN opens the whole subnet to their laptop. When does app-level access replace the VPN, and what still needs it?
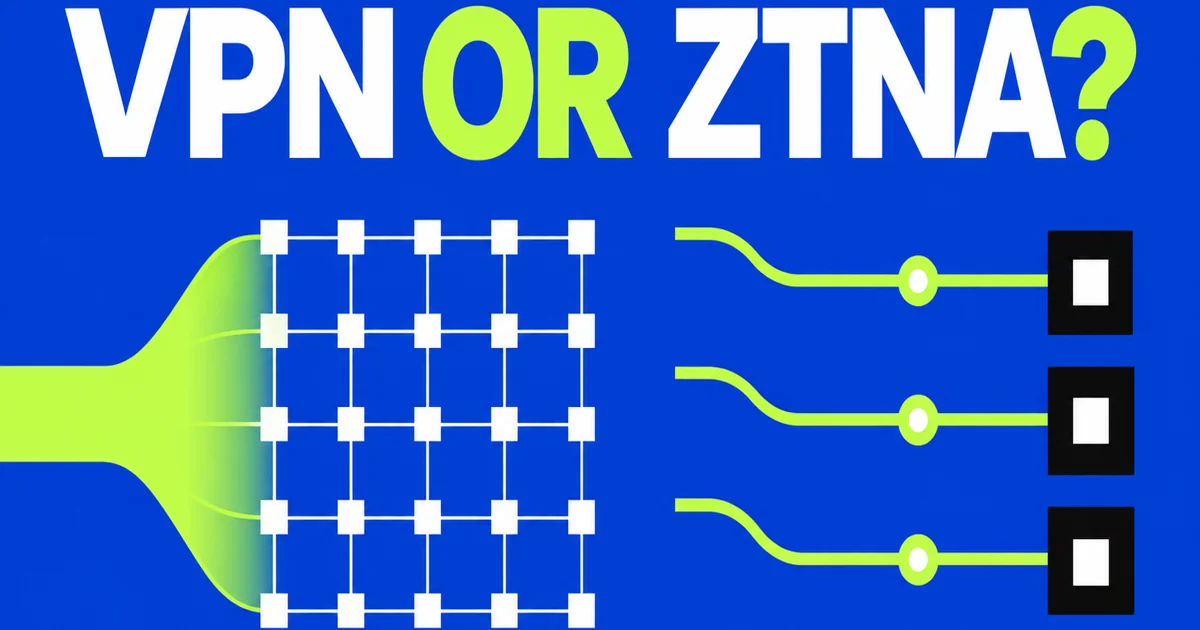
- A VPN connects a device to a network. ZTNA connects an approved user and device to a specific application.
- Cloud-first businesses should prefer ZTNA for internal web applications.
- Legacy file shares, broadcast protocols and broad administrator work may still require VPN access.
Remote access used to mean placing a laptop inside the office network through an encrypted tunnel. That solves transport. It does not automatically solve identity, device health, least privilege or visibility after connection.
The access boundary changes
| Business VPN | ZTNA | |
|---|---|---|
| Grants access to | Network or subnet | Named application |
| Primary decision | Credentials and tunnel | User, device, app and policy |
| Application exposure | Reachable through network | Brokered; often hidden |
| Lateral movement | Must be limited separately | Narrower by design |
| Legacy protocols | Strong compatibility | Product dependent |
ZTNA fits cloud-first work
Internal dashboards, admin panels, Git services and web applications can be published behind identity and device policy without opening an entire subnet. Access can be revoked by user, application or device posture, and logs map more directly to the resource used.
VPN still has legitimate work
Remote administrators may need SSH, RDP or several private services. Legacy applications may discover peers or assume local routing. A site-to-site tunnel may connect offices and cloud networks efficiently. Replacing these cases requires protocol testing, not a slogan.
Migration should reduce reach
- Inventory applications and protocols used through the VPN.
- Move web applications to app-specific access first.
- Require phishing-resistant MFA and managed-device posture.
- Keep a restricted VPN group for remaining legacy access.
- Measure active users and remove the broad tunnel when dependency reaches zero.
The decision
Use ZTNA as the default for application access and VPN as an explicit exception for network-level requirements. A zero-trust product does not create zero trust by itself; the value comes from narrow policy, strong identity and continuous device signals.