Cloudflare Tunnel Path Normalization: Does It Rewrite the Origin URL?
Your ingress rule matches the cleaned-up path, yet your app still receives the original slashes and dot segments. What does normalization touch, and when is it on by default?
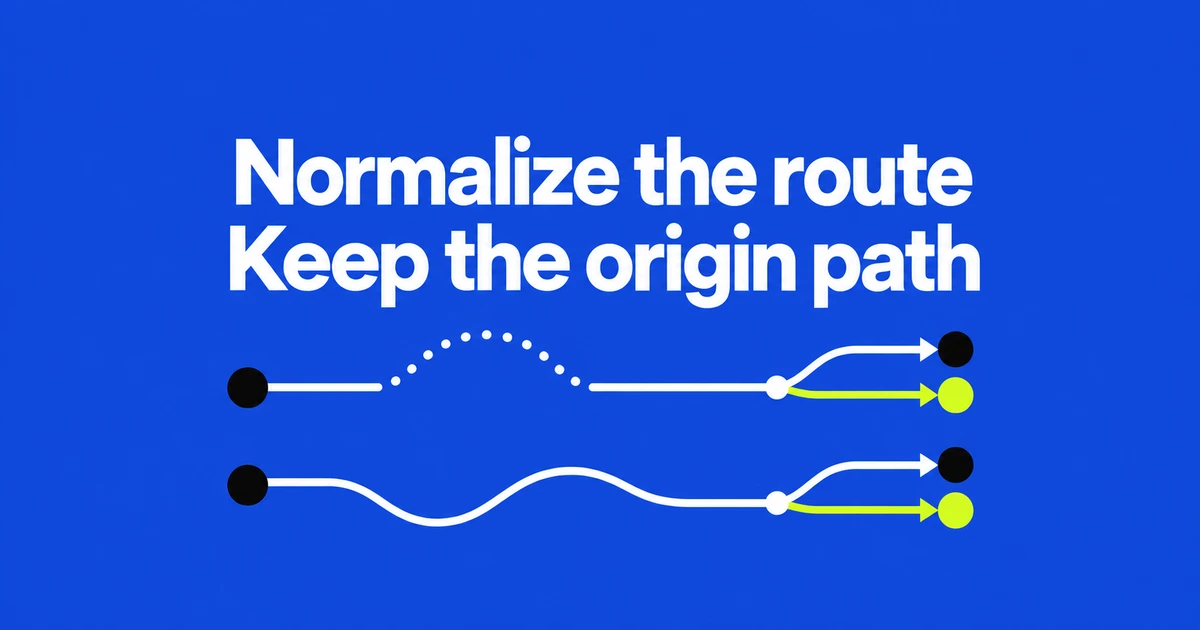
- Normalization changes ingress matching, not the request path forwarded by cloudflared.
- It applies to configurations containing rules that require Access validation.
- New releases from January 25, 2027 are scheduled to enable it by default.
A normalized match does not replace the origin path
Cloudflare Tunnel normalizes a path to choose an ingress rule. Its configuration reference separates that lookup from what the application receives:
| Received by cloudflared | Used to match rules | Forwarded to origin |
|---|---|---|
/hello/../path | /path | /hello/../path |
/hello//path | /hello/path | /hello//path |
/hello\path | /hello/path | /hello\path |
Enabling the feature can therefore select a different service without substituting the normalized path in the forwarded request. These examples begin where cloudflared receives the request; separate transformations earlier in the request chain remain separate settings.
Access validation determines whether normalization applies
The Access origin setting makes cloudflared validate the Access JWT before forwarding traffic. For configurations containing such rules, normalization resolves dot segments, converts backslashes and collapses repeated slashes.
The ingress implementation performs that operation before selecting the first matching rule. Its stated purpose is to prevent an earlier unprotected rule from capturing a traversal toward a protected path. Review the surrounding routing rules as well as the protected entry.
Configurations without rules requiring Access validation are unaffected by this change.
Set the disabling flag to false
The run-parameter reference requires cloudflared 2026.10.0 or later. To enable normalization, set the negatively named option to false:
cloudflared tunnel --disable-path-normalization=false run YOUR_TUNNELReplace the placeholder with an existing tunnel name or UUID. For a managed process, another option is to set TUNNEL_DISABLE_PATH_NORMALIZATION=false on each replica and restart it.
The October 22 announcement schedules a default change for new releases starting January 25, 2027. It does not say every existing installation will switch on that date.
Before upgrading, compare representative normal and alternate paths against the expected service and Access behavior. Check the request received by the application too: matching and application routing can interpret different forms of the same incoming path.
Removing /api is a different job
A route matching /api still forwards /api/users intact. Normalization is not a prefix-stripping feature.
If the backend expects /users, use a separate mechanism such as URL Rewrite Rules. A rewrite can change the URI path or query without redirecting the browser. Choose the setting according to the result you need: selecting a route or changing the URL delivered to the application.